
Access to other users' mailboxes
Version 2 of the September security update for Exchange Server was released on October 2, 2026. It adds the fix for CVE-2026-96940. Systems with the original September update therefore need another update.
The vulnerability allows an authenticated attacker to elevate privileges over the network and read messages and attachments from other mailboxes in the same organization. Microsoft rates it CVSS 8.8, severity Important. As of October 5, no active exploitation is known.
Installations that need the update
- Exchange Server SE RTM: KB5129955, version 15.02.2562.053.
- Exchange Server 2019 CU14/CU15 and 2016 CU23: corresponding V2 packages require enrollment in the Period 2 ESU program. Both product versions are out of regular support.
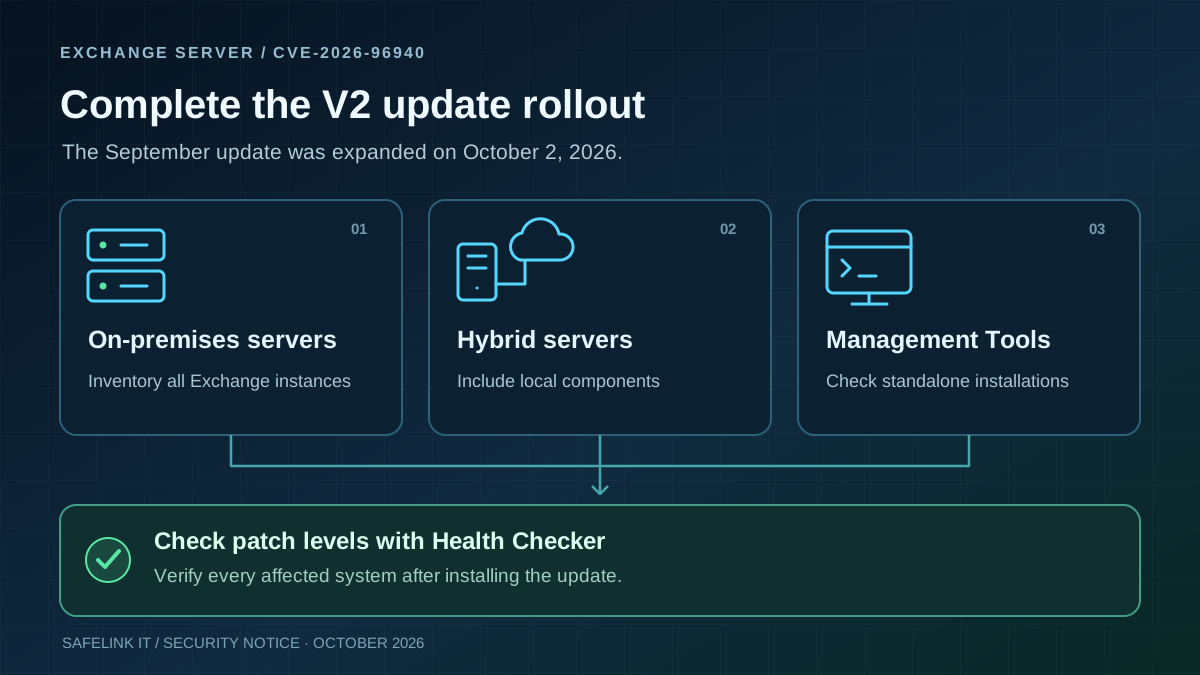
- Hybrid environments and management workstations: include local Exchange servers and installed Exchange Management Tools in the rollout. Exchange Online is protected at the service level; remaining on-premises components still need updating.
Verify installation and functionality
Deploy the package matching the installed Exchange version promptly during a maintenance window. For SE, the installation instructions recommend restarting before and after the update. Then run the current Exchange Server Health Checker to verify patch status and identify outstanding actions. Also test mail flow, sign-in and any hybrid features in use; track failed installations through to completion.
Documented issues for KB5129955 still include HTTP 500 errors with published ICS calendars and a possible ContentEngine deadlock caused by missing Korean WordBreaker files. Include these functions in the pilot where relevant. Suspicious mailbox access also requires investigation; installing the update does not establish whether data has already been read.