
Eight CA keys affected
Eight private keys belonging to subordinate eMudhra certificate authorities are compromised: six for TLS and two for code signing. Attackers could use them to impersonate services or make tampered software appear trustworthy. The incident concerns eMudhra's certificate hierarchy; Microsoft systems were not compromised.
Microsoft has blocked the affected keys since October 20, 2026 through the Windows disallowed list and, for TLS, a separate Edge/WebView2 component update. It also removed six eMudhra G3 roots and one AAA Certificate Services cross-sign certificate from its trust lists: on October 26 for Windows and October 27 for Edge. Blocking and removal are separate measures.
Updates must reach devices
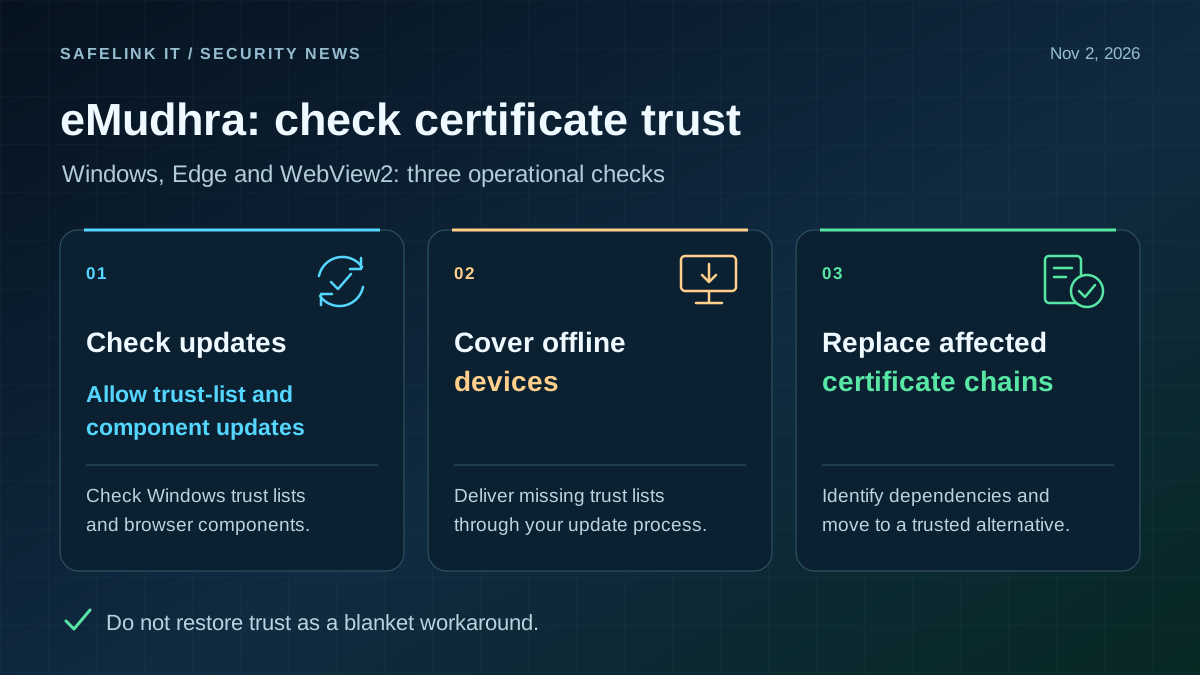
- Check Windows CTLs and Edge components. A successful WSUS patch cycle does not prove that Certificate Trust Lists (CTLs) are current; CTL distribution operates independently of WSUS. The Edge/WebView2 block does not require a new browser version.
- Cover disconnected devices separately. Deliver current trusted and disallowed CTLs through the designated internal distribution process. Include devices where policy disables automatic CTL updates.
- Assess the OOB update selectively. KB5134133 for Windows 11 24H2, 25H2 and 26H2 targets devices without current CTL updates. Installing it on Hotpatch devices interrupts Hotpatch until after the January 2027 baseline is installed.
Replace dependent certificates
Check certificate chains used by services and applications for the removed trust anchors and plan replacements. Do not routinely reimport removed roots to fix connection errors: software without reliable revocation checks could then continue accepting affected chains. After replacement, test connections and signature validation with the applications actually in use.