
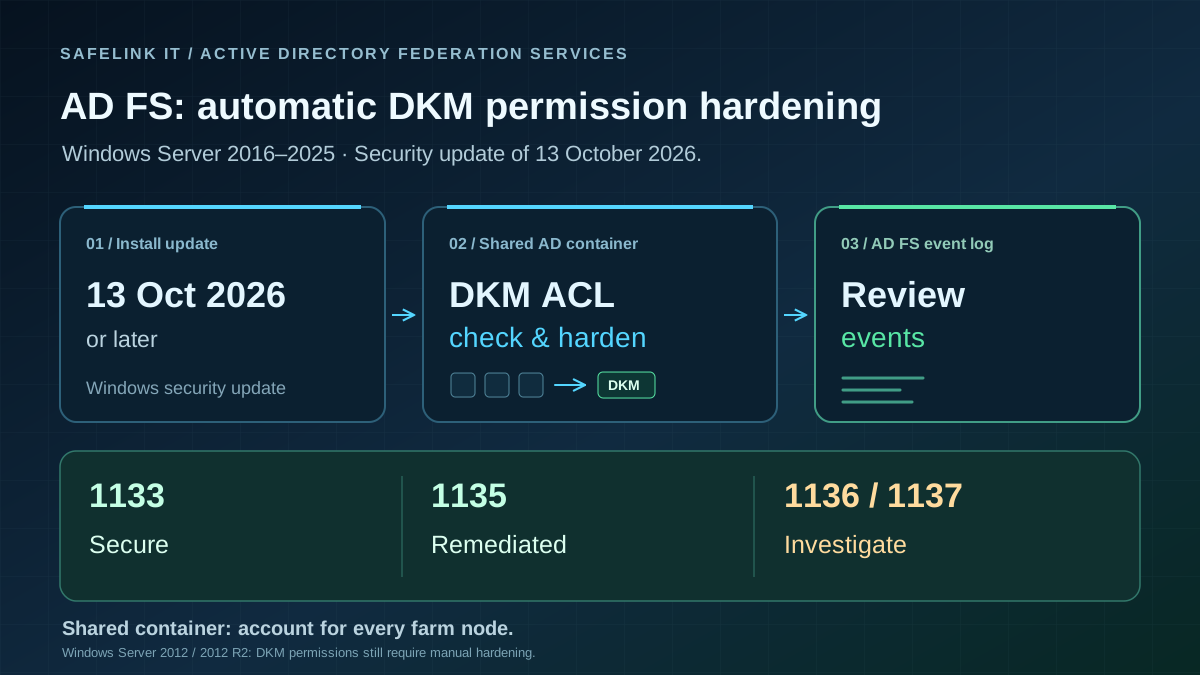
October update enables automatic remediation
The Windows security updates released on October 13, 2026 move AD FS DKM hardening from Audit to Enforcement. On Windows Server 2016, 2019, 2022 and 2025, AD FS now remediates insecure permissions on the Distributed Key Manager container by default. This change addresses CVE-2026-56155.
For existing farms, this is a significant operational change: review custom DKM permissions and potential sign-in impacts before rollout. Install the applicable October updates on every AD FS server, then test sign-in to connected applications.
Windows Server 2012 and 2012 R2 do not receive automatic remediation. Manual hardening remains necessary on these versions.
Check farm-wide settings and events
An existing RemediateDkmAcl=0 setting prevents automatic remediation on that server. All farm nodes share the same DKM container, so another updated node can still change the ACL. Review exceptions across the entire farm and avoid blanket disabling of hardening.
Check the AD FS/Admin log:
- 1133: the ACL matches the secure baseline.
- 1135: remediation succeeded; save the previous ACL from the associated 510 events with the same Instance ID.
- 1136/1137: remediation failed; 1137 indicates missing permissions to take ownership. Resolve the cause and verify the next check.