
Connecting media does not require an automatic launch
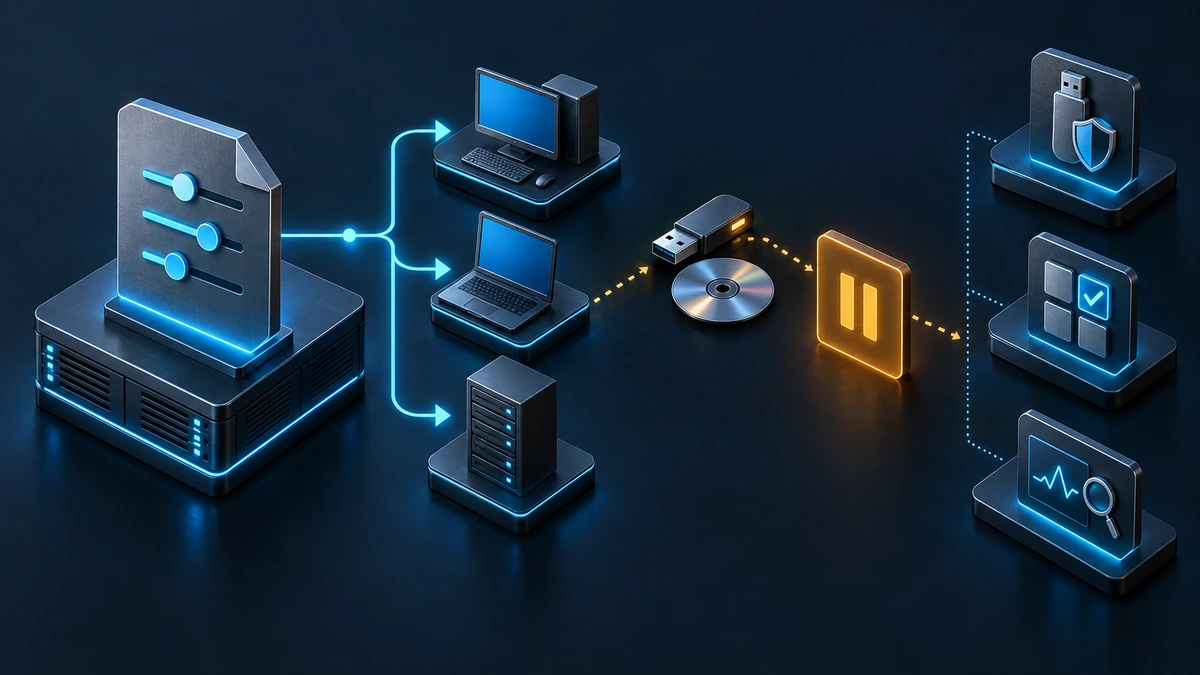
A support engineer attaches a drive, a department imports images from a camera and an administrator mounts installation media. Across an established Windows environment, user preferences, older GPOs and registered applications can determine which action is offered or launched automatically. Privileged workstations do not need this convenience; on standard clients it makes a consistent baseline harder to maintain.
AutoPlay and AutoRun are different functions. AutoPlay detects media or devices and offers appropriate actions or uses a saved choice. AutoRun concerns commands supplied through mechanisms such as an autorun.inf file. Modern Windows versions do not universally execute AutoRun programs when an ordinary USB drive is inserted: support for non-optical removable media was restricted many years ago. Optical media, other device types and AutoPlay handlers still warrant an explicit policy.
The connection to AD hardening is the central management of endpoints and administration systems. This measure reduces automatic media actions on computers used by domain accounts. It changes neither AD permissions nor the permissions of an attached device, and it does not replace control over executable files.
Target state: users deliberately initiate media access
The baseline establishes that managed systems do not require automatic media actions. Approved files and applications are opened through a documented manual procedure. Additional controls determine whether a device may be used and whether a file may execute.
- Standard clients: disable AutoPlay on all drives, prevent AutoRun commands and separately cover devices without a volume.
- Privileged admin workstations: apply the same baseline, complemented by narrowly scoped device approvals and application control. Untrusted media have no place in routine administration.
- Servers with a desktop interface: apply the baseline within the appropriate server GPO scope and test actual administration procedures. Installation media do not need to launch automatically.
- Special-purpose workstations: test camera imports, measurement equipment and other justified cases before rollout. Exceptions receive an owner, a narrow device scope and an expiry date.
A desktop AutoPlay test is not meaningful on Server Core. Assess the applicable configuration and the device and execution paths actually present separately. The absence of a shell feature does not prove that removable media are blocked.
Three settings form the Group Policy baseline
A dedicated computer GPO makes ownership visible and rollback traceable. In Group Policy Management, the path is Computer Configuration > Policies > Administrative Templates > Windows Components > AutoPlay Policies. Labels can vary slightly with the language and ADMX version.
1. Turn off AutoPlay on all drives
Set “Turn off Autoplay” to Enabled and select “All drives”. Choosing only the narrower set of drive types does not fully implement the target state.
The computer policy sets NoDriveTypeAutoRun under HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\Explorer to 255, or 0xFF. For this AutoPlay policy, the computer setting takes precedence over a conflicting user setting. Assigning it to computers also avoids making protection dependent solely on the signed-in user's OU.
2. Explicitly prevent AutoRun commands
Set “Set the default behavior for AutoRun” to Enabled and select “Do not execute any autorun commands”.
The expected value is NoAutorun = 1 under the same registry path. The selection matters: an “Enabled” status alone does not describe the intended behaviour. An option that automatically executes AutoRun commands would produce the opposite result.
3. Include devices without a volume
Set “Disallow Autoplay for non-volume devices” to Enabled. This covers devices such as suitable cameras or smartphones using MTP that do not appear as a normal drive.
This setting writes NoAutoplayfornonVolume = 1 under HKLM\SOFTWARE\Policies\Microsoft\Windows\Explorer. The different path is a common source of inventory errors. The policy does not universally block the device or access to its data.
Test the rollout against real working procedures
Before making changes, inventory existing computer and user policies, GPO links, security filters and any MDM settings. On co-managed devices, the setting needs an explicitly assigned owner. Competing management channels should not determine the baseline through whichever update happens to arrive last.
- Record the starting state: back up affected GPOs and document policy results and required media procedures. Existing registry values alone do not explain their origin.
- Build a small pilot: include a standard client, an admin workstation and a relevant specialist workstation; handle servers separately. Account for supported Windows versions and the ADMX files in use.
- Assign the computer GPO: configure all three settings, link it deliberately and wait for normal policy processing or refresh the pilot devices. For an existing desktop session, also repeat the test after signing in again.
- Use approved test media: test a known USB drive, optical media or an approved mounted image, and a relevant MTP device where these exist in production. Do not use unknown media or test programs with harmful functionality.
- Accept the business procedures: automatic actions stay suppressed while approved manual imports or access still work. Check whether a vendor application runs its own import service instead of using Windows AutoPlay.
- Roll out in waves: provide helpdesk instructions, measurable coverage and a rollback procedure. A disrupted critical import process stops the next wave until its cause and a replacement procedure are resolved.
Exceptions belong in a targeted scope. Removing the baseline across the domain because one camera application needs adjustment would be a disproportionate reversal.
Verify effectiveness with three forms of evidence
First use gpresult /scope computer /r, or a securely stored Group Policy Results report, to check that the intended computer GPO applies. Then examine the effective values on the target device and run a functional test with the media actually used. Reports contain internal names and group information and belong in protected project storage.
The following local PowerShell check only reads the three computer settings. It changes neither GPOs nor registry values and distinguishes an absent value from an explicitly configured zero:
Set-StrictMode -Version Latest
$ErrorActionPreference = 'Stop'

$legacy = 'HKLM:\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\Explorer'
$modern = 'HKLM:\SOFTWARE\Policies\Microsoft\Windows\Explorer'
$checks = @(
    @{ Path = $legacy; Name = 'NoDriveTypeAutoRun'; Expected = 255 }
    @{ Path = $legacy; Name = 'NoAutorun'; Expected = 1 }
    @{ Path = $modern; Name = 'NoAutoplayfornonVolume'; Expected = 1 }
)

foreach ($check in $checks) {
    try {
        $actual = $null
        if (Test-Path -LiteralPath $check.Path) {
            $item = Get-ItemProperty -LiteralPath $check.Path
            $property = $item.PSObject.Properties[$check.Name]
            if ($null -ne $property) { $actual = $property.Value }
        }
        [pscustomobject]@{
            Setting = $check.Name
            Value = $actual
            Expected = $check.Expected
            MatchesBaseline = ($null -ne $actual -and $actual -eq $check.Expected)
        }
    } catch {
        throw "Cannot read policy setting: $($check.Name)."
    }
}
A matching value proves the local configuration, but not its continued management or the success of every functional test. An absent value means that the explicit computer baseline has not been demonstrated; it does not automatically mean Windows permits every media action. User policies and operating system defaults may also apply.
The AutoPlay switch in Windows Settings is not reliable compliance evidence. It may remain editable even when Group Policy is enforced. Policy results, configured values and observed behaviour are the relevant checks.
Benefits of centrally disabling automatic actions
- Automatic media actions and saved AutoPlay choices can be consistently suppressed; privileged sessions in particular do not need this feature.
- The same computer baseline applies regardless of which domain user signs in. Deviations can be inventoried centrally.
- Implementation requires no additional software and can use existing GPO deployment, verification and documentation processes.
- Approved manual media access generally remains available where other policies allow it. This makes a targeted rollout easier than a complete device ban.
Disadvantages and clear protection limits
- Camera imports, installation procedures and other convenience functions may require extra manual steps. Dependent business applications create testing and support work.
- This measure does not prevent someone from manually launching a file, opening malicious document content or encountering filesystem or driver vulnerabilities. It does not assess whether a file is trustworthy.
- A USB device presenting itself as a keyboard or network adapter is not generally blocked by these AutoPlay settings. Appropriate device and interface controls are required for that purpose.
- Third-party applications may use their own detection or import services. Their behaviour needs separate configuration.
- Current systems already restrict classic USB AutoRun. The added value is a complete, explicit baseline; the change does not universally eliminate an automatic execution path that was previously open everywhere.
Application control, EDR, least privilege and appropriate device control remain separate project components. Administrative workstations also need a defined process for obtaining software and installation media from trusted sources.
Common mistakes in verification and rollback
A common mistake is relying entirely on a user GPO: another sign-in context or a local administrator account may fall outside the intended scope. Selecting only some drive types, overlooking the non-volume policy and checking every value under a single registry key also leave the implementation incomplete.
Another incorrect diagnosis occurs when files remain accessible after the change. That can be exactly the intended result: automatic actions are suppressed, while data transfer is not necessarily blocked.
For rollback, restore the documented previous policy configuration within the affected scope and test it again. “Not configured” does not guarantee that the precise earlier state returns; other GPOs, MDM requirements or previous manual settings may take effect. GPO backups, local values and functional tests therefore also belong in the recovery procedure.
Project acceptance checklist
- [ ] Windows versions, device classes and relevant media procedures are inventoried.
- [ ] Computer GPO scope, ownership and potential MDM overlap are resolved.
- [ ] “Turn off Autoplay” is enabled and set to “All drives”.
- [ ] AutoRun commands are explicitly prevented and non-volume devices are covered.
- [ ] All three expected values have been checked at the correct registry paths.
- [ ] Policy results and harmless functional tests demonstrate effectiveness in the pilot.
- [ ] Approved manual access and critical import procedures have passed acceptance testing.
- [ ] Device access and application control are assessed separately.
- [ ] Exceptions have a scope, an owner and an expiry date.
- [ ] Helpdesk guidance, rollout waves, coverage checks and rollback are prepared.